Secrets
API keys, passwords and private keys in your code.
Automated code scanning on every push, with findings as bugs on your board
On every push Kantex scans the changed lines for secrets, injection, insecure connections and leftover debug code. Add KantexAI for a second, deeper review. From the severity you choose, a finding becomes a bug, and the next push does not create a duplicate.
Included from the Business plan, €13 per user per month
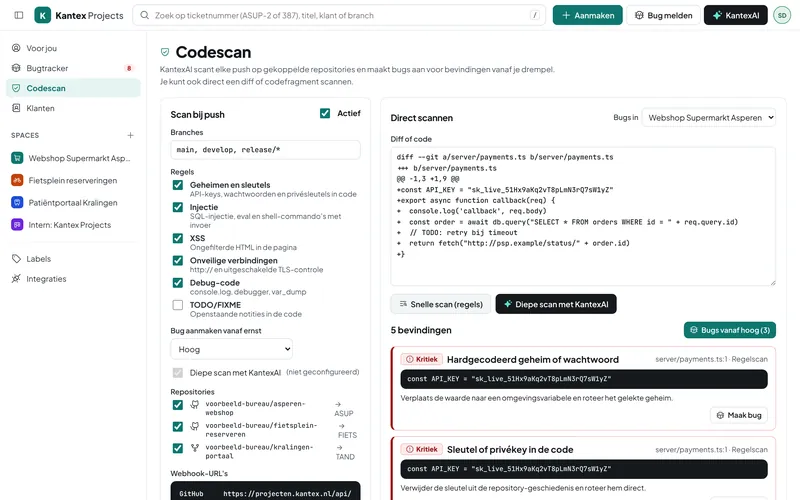
Choose the rules, the branches to scan and the severity at which a bug is created.
On every push Kantex fetches the changes and scans only the lines that changed.
Findings above your threshold appear as bugs on the board, with file, line and a suggestion.
API keys, passwords and private keys in your code.
SQL built from input, eval, shell commands and unescaped HTML.
http:// and disabled TLS verification.
console.log, debugger and var_dump that would otherwise ship.
A second review with an explanation and a suggested fix.
Scan only main, or feature branches too. You choose the pattern.
No. The code scan catches common mistakes early, on every push. For a full audit or penetration test you still need a specialist.
Yes. On Free and Team you can add the code scan for €29 per month. It is included in Business.
Only if you switch on the KantexAI scan. The rule-based scan runs entirely within Kantex Projects itself.
Every feature, your own environment and a free switching service. No credit card needed.